When Did That Service Account Last Rotate? (Part 5 of 6)
gMSA and dMSA reduce service-account risk through automatic password management and machine-bound use. They still require protected LDAP transport and least privilege.
Are You Hoping Your LDAP Is Secure – or Do You Know? (Part 6 of 6)
A complete LDAP migration starts with auditing, then secures the channel, bind, and account before enforcing signing and channel binding and validating the result.
There are three ways BYOD quietly becomes your biggest security liability — and only one of them shows up on a device audit.
BYOD risk usually comes from an outdated policy, limited visibility into app behavior, and misplaced trust in how employees handle corporate data on personal devices.
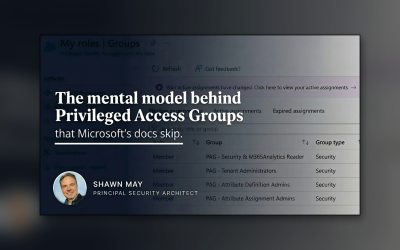
The layer Microsoft’s docs never show you.
Privileged Access Groups work in layers: security groups hold permissions, PIM makes membership eligible, activation grants time-bound access, and some directory roles require a second activation.
Blocking USB Storage Does Not Block USB Security Keys
A USB storage block targets mass-storage devices. FIDO2 security keys use the Human Interface Device protocol, so they require separate endpoint and Entra ID policy design.

When MFA Registration Gets Confusing, Here’s Why
Most MFA registration problems are not really MFA problems. One user is brand new and needs to register their first method. Another already has MFA, Windows Hello for Business, FIDO2, etc. and just wants to update…
The Secret Trio Behind Email Security: Why SPF, DKIM, and DMARC Are Essential
Picture this: You check your phone one morning to find your inbox flooded with panicked messages. Someone’s been sending sketchy emails pretending to be your company, and now your customers are freaking out. Unfortunately, this nightmare…

Stop Wasting Time on Your Cybersecurity Hiring Search – Focus on What Really Matters
Let’s be honest – finding great cybersecurity talent is tough. But instead of getting caught up in an endless resume hunt, I’ve found it’s better to focus on the qualities that truly indicate someone will excel…

Enable Safe Links in Microsoft Defender for Office 365
Why this matters: Phishing emails are not always obvious. In fact, many look like they came from a trusted colleague or a legitimate service you use every day. The real danger is in the hidden links.…
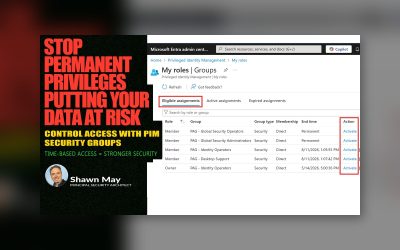
How to implement privileged time-based access controls.
Is Your Organization Handing Out Permanent Privileges to Attackers? That may sound dramatic, but every security breach involving stolen credentials shares one truth: the attacker did not need 24/7 administrative access… until they had it. The…
Conditional Access Break-Glass Accounts: Would Yours Still Get You In?
Conditional Access break-glass accounts can quietly stop working as Microsoft changes the...


