Your MFA Is On. Is It Actually Covering You?
MFA can be switched on and still fail the test that matters. Learn how phishing-resistant MFA, token protection, risk-based controls, and provable evidence separate “on” from truly covered.
MFA can be switched on and still fail the test that matters. Learn how phishing-resistant MFA, token protection, risk-based controls, and provable evidence separate “on” from truly covered.
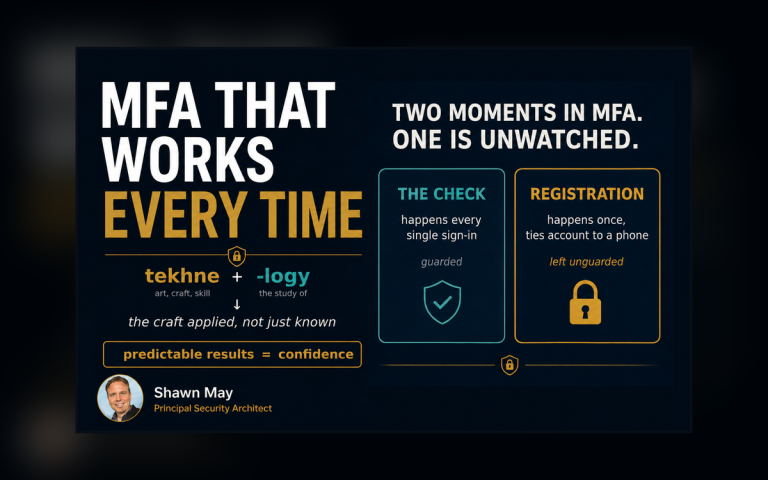
The registration step most people skip Turning on multi-factor authentication feels like the job is finished. For almost every account, it is.
A conditional access policy is the rule in Microsoft Entra that decides who gets in, to what, under which conditions, and what they must prove first.
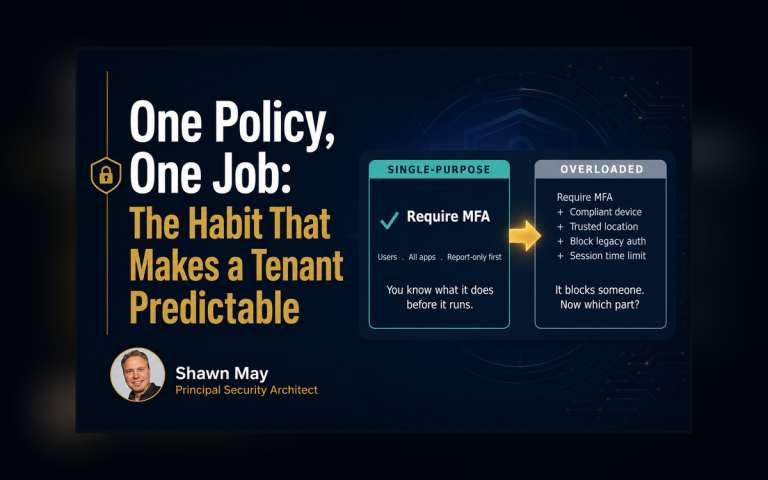
You get the ticket. A user’s blocked and they need in now. You open the policy that caught them, and it’s doing five things at once.
A Conditional Access exclusion is any user, group, role, or app you leave out of a policy, so that policy’s control doesn’t apply to them.

Conditional Access is Microsoft Entra’s policy engine for sign-in decisions. It gathers signals about a sign-in, who it is, what app, what device, where from, how risky, then matches them against your rules and enforces…
Explore how Entra ID Conditional Access uses dynamic policy signals to safeguard your digital assets, ensuring only authorized access through intelligent decision-making.