Conditional Access Break-Glass Accounts: Would Yours Still Get You In?
Conditional Access break-glass accounts can quietly stop working as Microsoft changes the platform. See what your technologists need to know.

Most Conditional Access Is Learned by Trial and Error
Most Conditional Access is learned by trial and error, often in production. See how Conditional Access Foundation teaches the fundamentals first.
Are Your Cybersecurity Skills Getting Sharper, or Just Older?
A cybersecurity skill is a craft that compounds when you practice it and fades when you don’t. How security teams keep theirs sharp.

Security Control Decay: The Risk You Already Signed Off On
Security control decay is the risk you already signed off on. How a control rots across handoffs, why it matters to a CISO, and how to stop it.
Phishing-Resistant MFA for Admins Without the Lockout
Phishing-resistant MFA for admins is stronger than codes. Roll it out in stages, protect emergency access, and avoid locking out your team.
Your MFA Is On. Is It Actually Covering You?
MFA can be switched on and still fail the test that matters. Learn how phishing-resistant MFA, token protection, risk-based controls, and provable evidence separate “on” from truly covered.
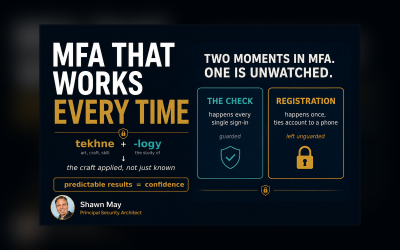
MFA That Works Every Time
The registration step most people skip Turning on multi-factor authentication feels like the job is finished. For almost every account, it is.
How to Read a Conditional Access Policy Without Trusting the Name
A conditional access policy is the rule in Microsoft Entra that decides who gets in, to what, under which conditions, and what they must prove first.

The Scapegoat After the Breach
For the security leader who owns the risk Somewhere in your files is a form with your name on it. An insurance application, a customer questionnaire, a board attestation. One line says MFA is enforced.
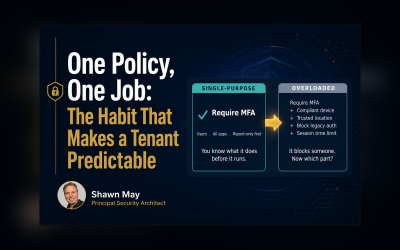
One Policy, One Job: The Habit That Makes a Tenant Predictable
You get the ticket. A user’s blocked and they need in now. You open the policy that caught them, and it’s doing five things at once.
Conditional Access Break-Glass Accounts: Would Yours Still Get You In?
Conditional Access break-glass accounts can quietly stop working as Microsoft changes the...


