Eligible, Not Active: Why PIM-Enabled Groups Are the Right Way to Hold a Role
PIM-enabled groups should make users eligible, not permanently active. Activation should be time-limited, logged, and monitored for direct additions that bypass PIM.
PIM-enabled groups should make users eligible, not permanently active. Activation should be time-limited, logged, and monitored for direct additions that bypass PIM.
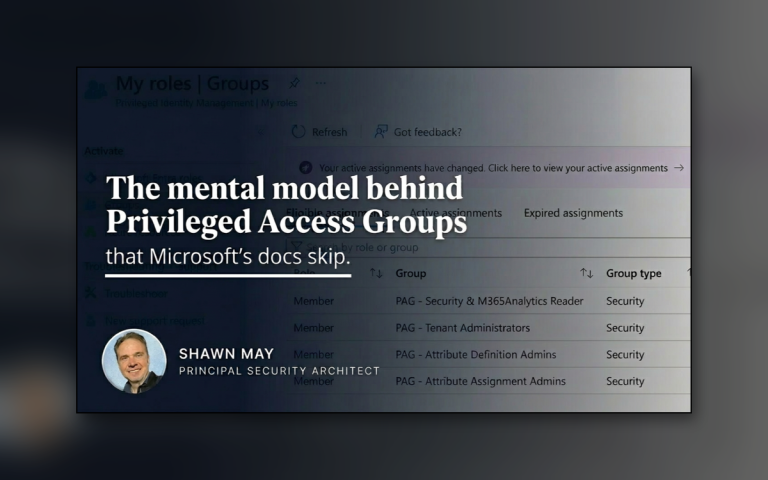
Privileged Access Groups work in layers: security groups hold permissions, PIM makes membership eligible, activation grants time-bound access, and some directory roles require a second activation.
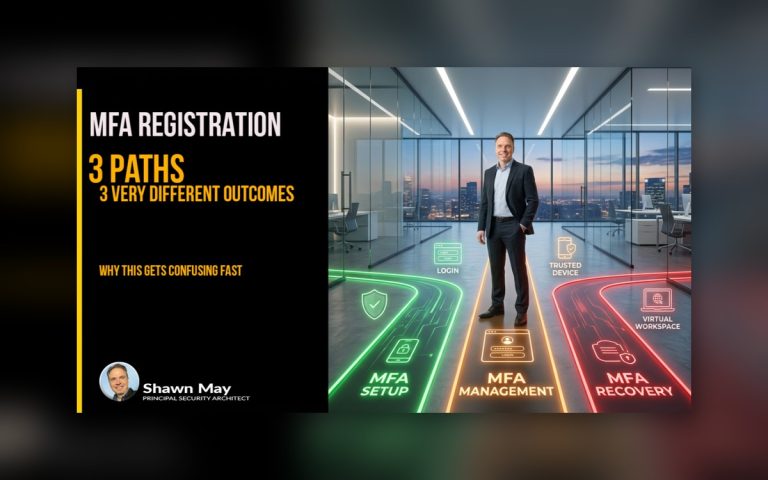
Most MFA registration problems are not really MFA problems. One user is brand new and needs to register their first method. Another already has MFA, Windows Hello for Business, FIDO2, etc. and just wants to update…
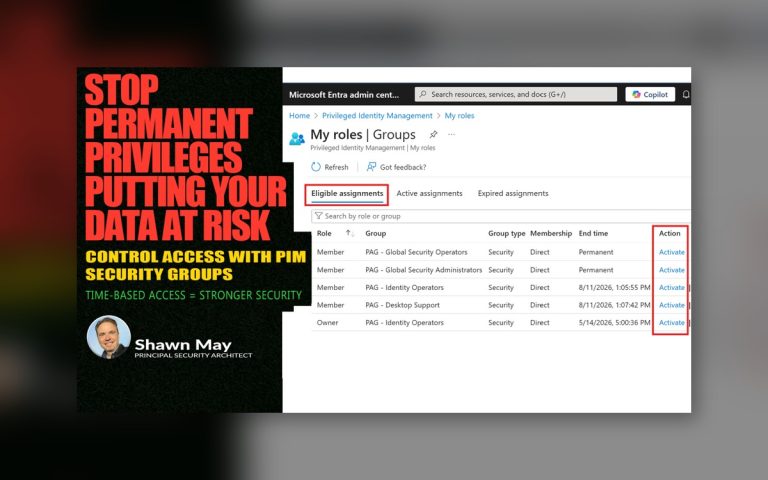
Is Your Organization Handing Out Permanent Privileges to Attackers? That may sound dramatic, but every security breach involving stolen credentials shares one truth: the attacker did not need 24/7 administrative access… until they had it. The…
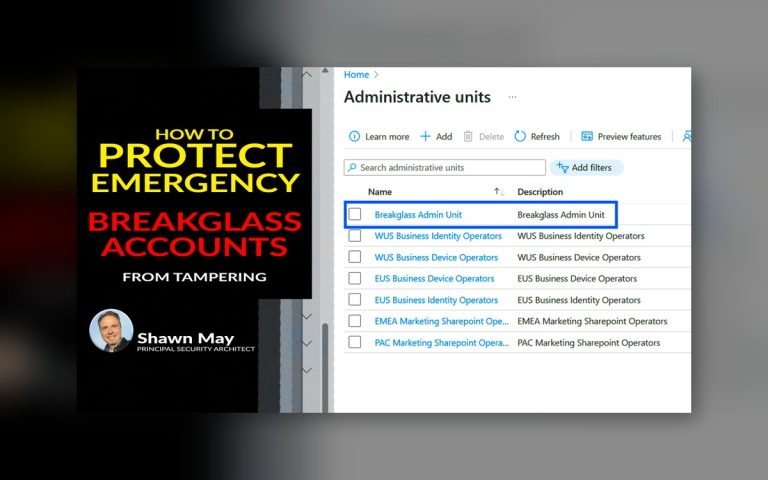
How can Restricted Management Administrative Units enhance the security of BreakGlass accounts? BreakGlass accounts are critical for emergency access but pose significant security risks if not properly managed. By leveraging Admin Units with restricted management, you…
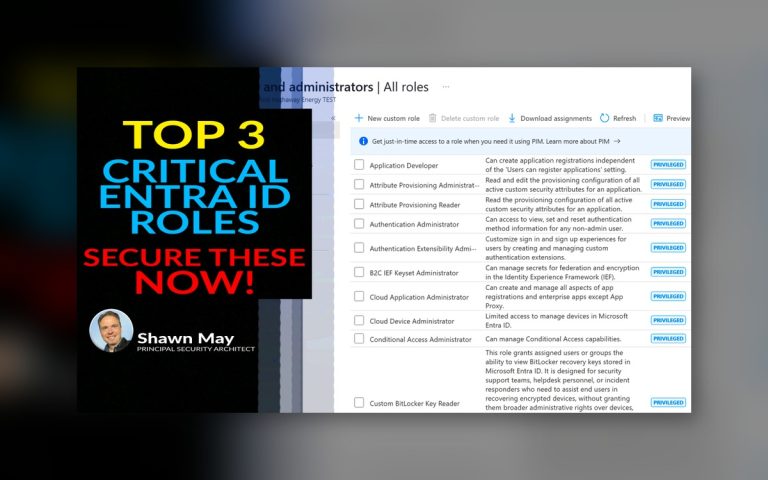
As a Microsoft cloud security expert, one of the most common questions I get is: “What roles should we lock down first in our Entra ID environment?” My answer is always the same: start with your…
This topic routinely comes up: why does Office continue asking for credentials, or what’s actually required for SSO on Windows? The details can be a mess. After talking with a lot of users and researching recent…
This isn’t just a flowchart – it’s a mindset shift. If you’re serious about controlling access, enforcing compliance, and locking down attack surfaces, then understanding device trust is non-negotiable. This logic flow decodes how Entra ID…
In the first part of this series ( read Part 1 ), we examined the risks associated with improper management of privileged access and the vulnerabilities it creates within an organization. We also introduced the concept…
As a cloud security consulting group, one of our core responsibilities is to identify potential security vulnerabilities that could compromise a business’s operations and recommend actionable, proactive measures to address them. Among these vulnerabilities, one recurring…