Is Your Domain Controller Leaking Passwords? (Part 2 of 6)
Cleartext or unsigned LDAP simple binds expose reusable passwords. Event IDs 2887 and 2889 identify the affected volume, clients, and accounts before enforcement.
Use to show article snippet on Know the Security Risks page.
Cleartext or unsigned LDAP simple binds expose reusable passwords. Event IDs 2887 and 2889 identify the affected volume, clients, and accounts before enforcement.
SASL with Kerberos replaces a reusable LDAP password with a short-lived ticket. Signing and channel binding then protect that authentication from tampering and relay.
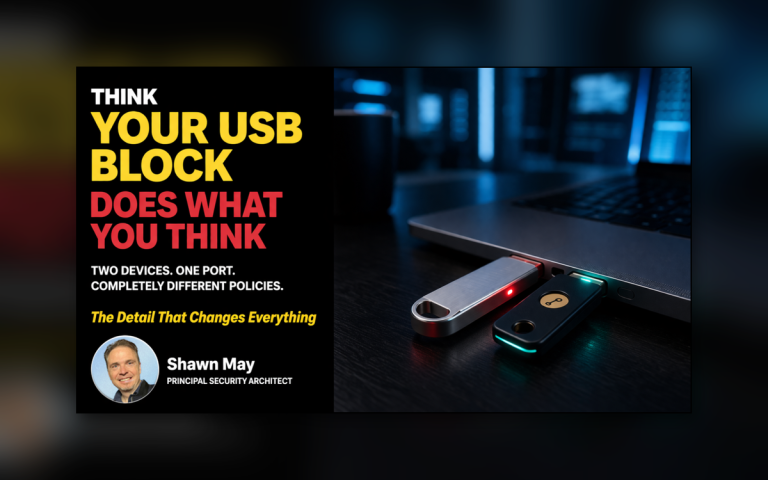
A USB storage block targets mass-storage devices. FIDO2 security keys use the Human Interface Device protocol, so they require separate endpoint and Entra ID policy design.
Picture this: You check your phone one morning to find your inbox flooded with panicked messages. Someone’s been sending sketchy emails pretending to be your company, and now your customers are freaking out. Unfortunately, this nightmare…
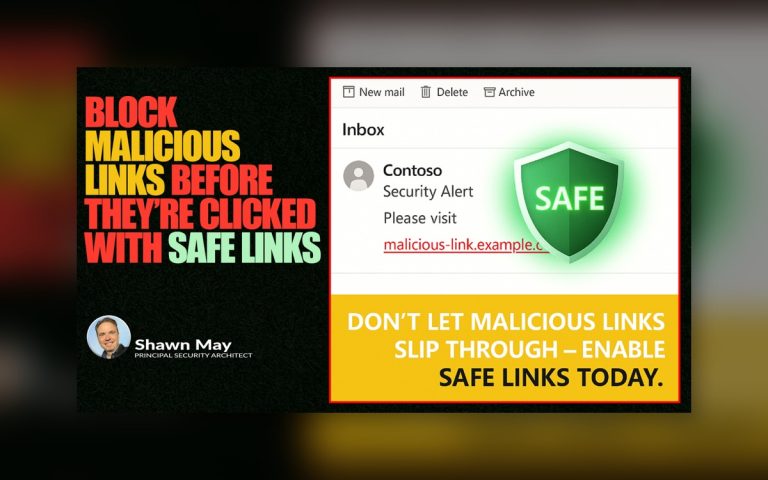
Why this matters: Phishing emails are not always obvious. In fact, many look like they came from a trusted colleague or a legitimate service you use every day. The real danger is in the hidden links.…
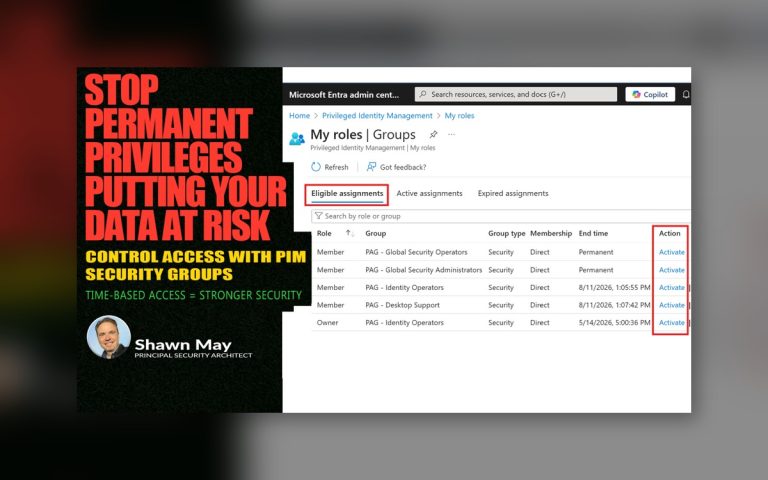
Is Your Organization Handing Out Permanent Privileges to Attackers? That may sound dramatic, but every security breach involving stolen credentials shares one truth: the attacker did not need 24/7 administrative access… until they had it. The…
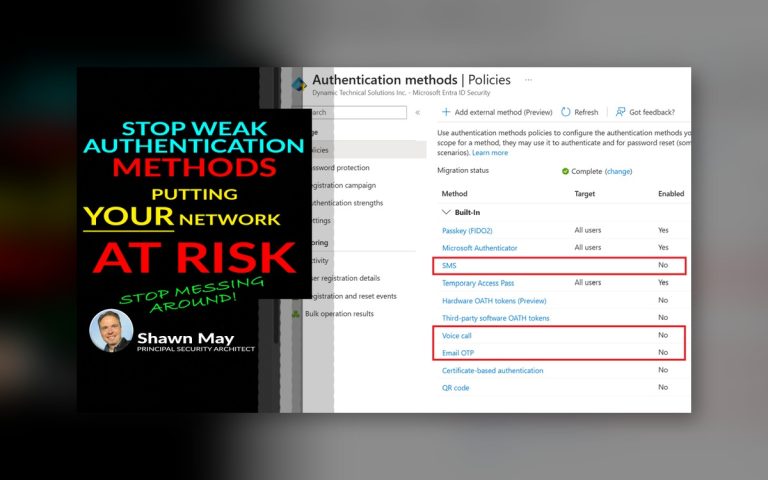
Are business users still relying on insecure authentication methods like SMS, voice calls, or email one-time passwords? At DTS, we strongly recommend moving away from these vulnerable options toward stronger, more secure methods that meet the…
How can Restricted Management Administrative Units enhance the security of BreakGlass accounts? BreakGlass accounts are critical for emergency access but pose significant security risks if not properly managed. By leveraging Admin Units with restricted management, you…
As a Microsoft cloud security expert, one of the most common questions I get is: “What roles should we lock down first in our Entra ID environment?” My answer is always the same: start with your…
This isn’t just a flowchart – it’s a mindset shift. If you’re serious about controlling access, enforcing compliance, and locking down attack surfaces, then understanding device trust is non-negotiable. This logic flow decodes how Entra ID…