You Don’t Need to Manage the Phone. You Need to Manage the Data.
For personal phones, Mobile Application Management protects corporate data inside approved apps without enrolling the entire device. Full MDM fits company-owned devices.
Use to show article snippet on Best Practices in CyberSecurity page.
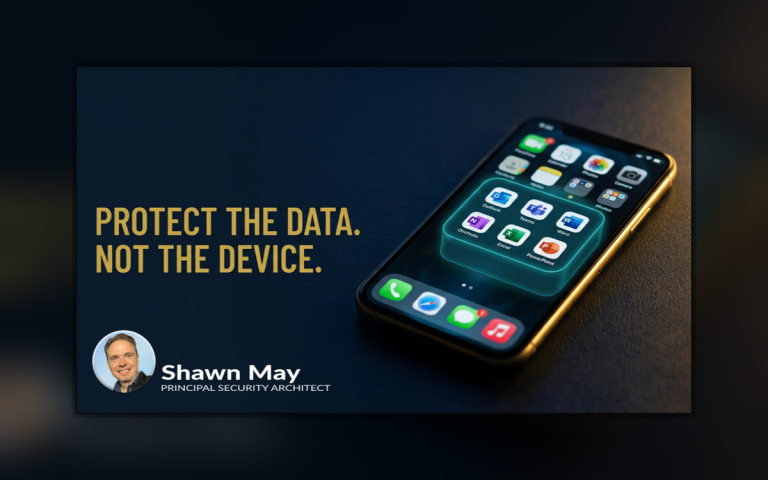
For personal phones, Mobile Application Management protects corporate data inside approved apps without enrolling the entire device. Full MDM fits company-owned devices.
PIM-enabled groups should make users eligible, not permanently active. Activation should be time-limited, logged, and monitored for direct additions that bypass PIM.
BYOD risk usually comes from an outdated policy, limited visibility into app behavior, and misplaced trust in how employees handle corporate data on personal devices.
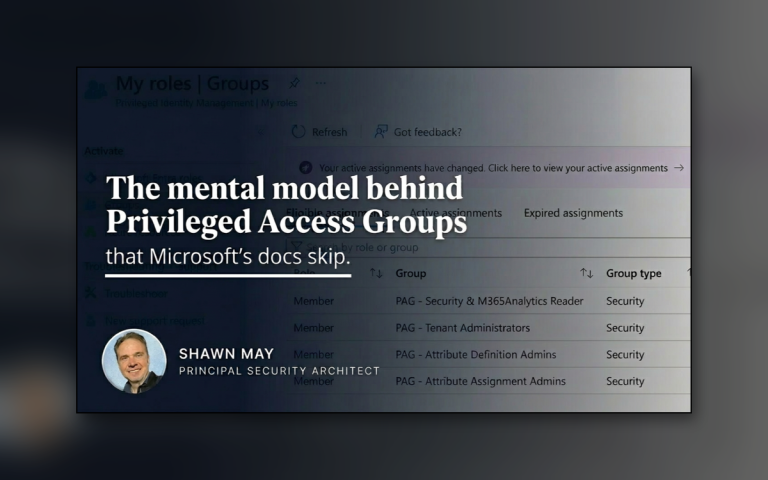
Privileged Access Groups work in layers: security groups hold permissions, PIM makes membership eligible, activation grants time-bound access, and some directory roles require a second activation.
A USB storage block targets mass-storage devices. FIDO2 security keys use the Human Interface Device protocol, so they require separate endpoint and Entra ID policy design.
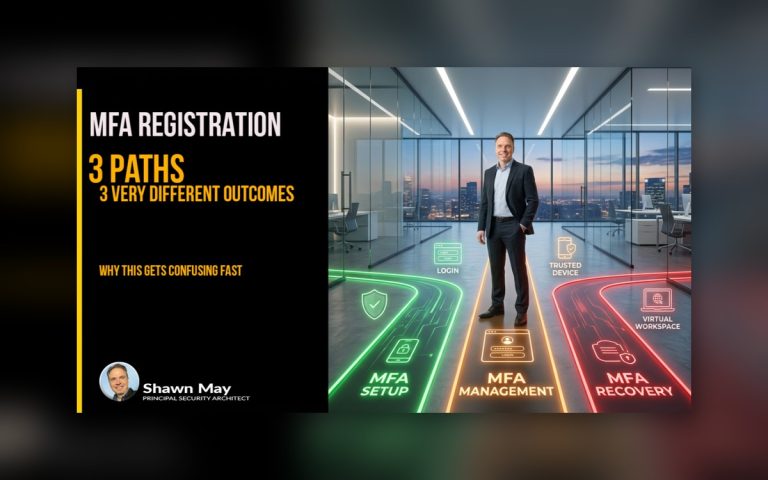
Most MFA registration problems are not really MFA problems. One user is brand new and needs to register their first method. Another already has MFA, Windows Hello for Business, FIDO2, etc. and just wants to update…
Picture this: You check your phone one morning to find your inbox flooded with panicked messages. Someone’s been sending sketchy emails pretending to be your company, and now your customers are freaking out. Unfortunately, this nightmare…
Let’s be honest – finding great cybersecurity talent is tough. But instead of getting caught up in an endless resume hunt, I’ve found it’s better to focus on the qualities that truly indicate someone will excel…
Why this matters: Phishing emails are not always obvious. In fact, many look like they came from a trusted colleague or a legitimate service you use every day. The real danger is in the hidden links.…
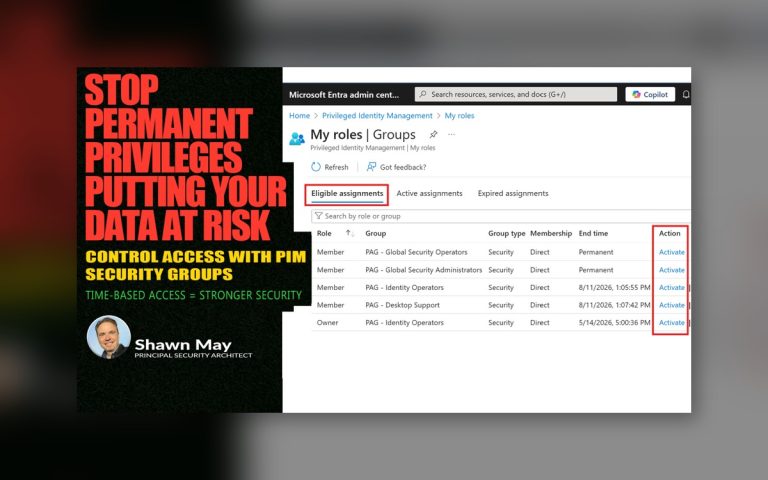
Is Your Organization Handing Out Permanent Privileges to Attackers? That may sound dramatic, but every security breach involving stolen credentials shares one truth: the attacker did not need 24/7 administrative access… until they had it. The…