One Policy, One Job: The Habit That Makes a Tenant Predictable
You get the ticket. A user’s blocked and they need in now. You open the policy that caught them, and it’s doing five things at once.
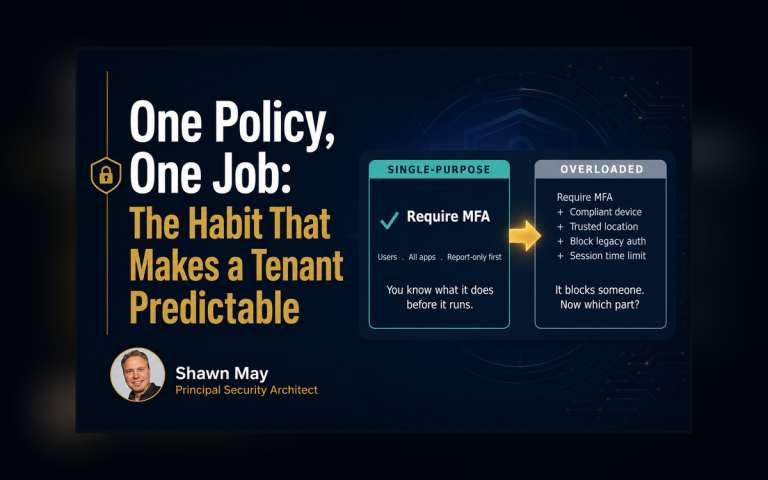
You get the ticket. A user’s blocked and they need in now. You open the policy that caught them, and it’s doing five things at once.
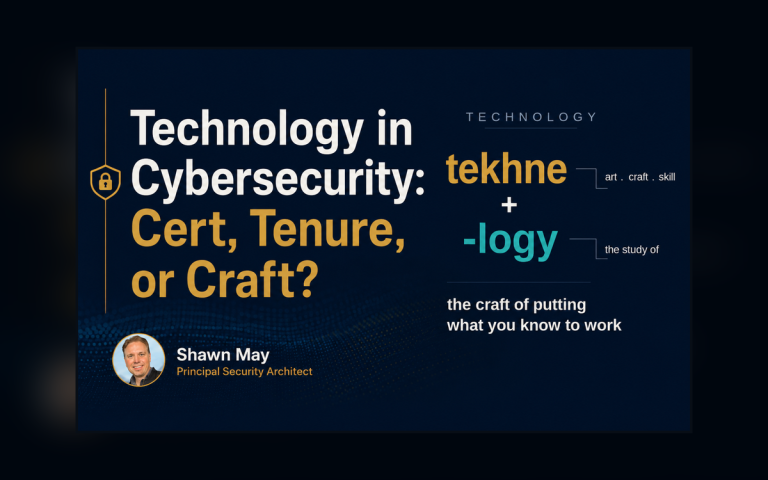
In cybersecurity hiring, two signals mislead us. A certificate proves someone studied, and tenure proves they showed up for years. Neither proves craft, the skill to apply the work when an incident goes off-script.
A Conditional Access exclusion is any user, group, role, or app you leave out of a policy, so that policy’s control doesn’t apply to them.

Conditional Access is Microsoft Entra’s policy engine for sign-in decisions. It gathers signals about a sign-in, who it is, what app, what device, where from, how risky, then matches them against your rules and enforces…
Picture it. It’s a Tuesday. A good client is on the line and their voice is a little off. “Quick question. Why did your bank details change on the last invoice?” You didn’t change anything. That’s the moment it lands.
For personal phones, Mobile Application Management protects corporate data inside approved apps without enrolling the entire device. Full MDM fits company-owned devices.
PIM-enabled groups should make users eligible, not permanently active. Activation should be time-limited, logged, and monitored for direct additions that bypass PIM.
LDAP security is three separate jobs: encrypt the connection, strengthen the authentication method, and secure the account. Enabling LDAPS completes only the first job.
LDAPS and StartTLS can protect LDAP traffic equally when correctly enforced. Protection fails when StartTLS falls back to cleartext or weak TLS remains enabled.
SASL with Kerberos replaces a reusable LDAP password with a short-lived ticket. Signing and channel binding then protect that authentication from tampering and relay.